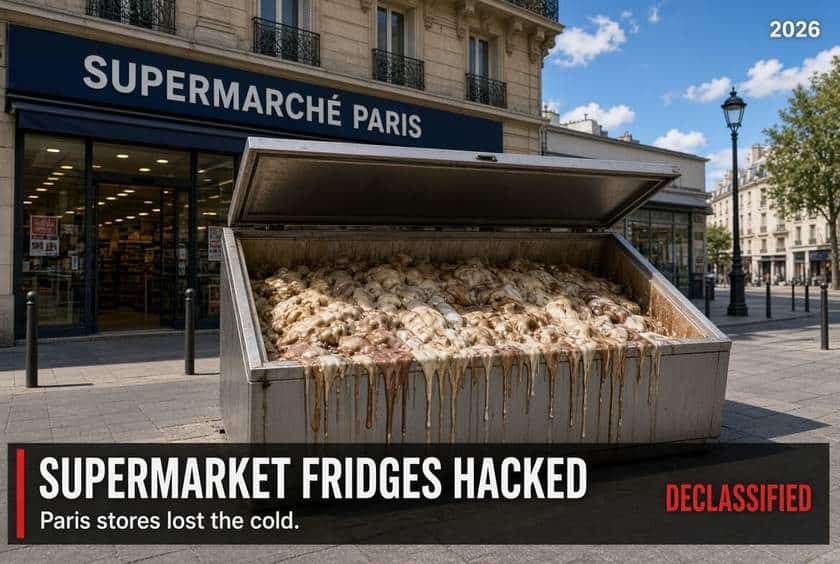
On Monday morning, staff at an Intermarché in central Paris were tipping cartfuls of thawed frozen food into a giant trash container on the street, with melted ice cream running out of the broken tubs, a witness told Reuters. Overnight, the refrigerators and freezers at about 150 of the chain’s stores had been heated to 50 degrees Celsius (122 degrees Fahrenheit) for six hours, according to its owner, Les Mousquetaires. Everything affected was thrown out.
Intermarché wasn’t alone. The Paris prosecutor’s office confirmed a “large-scale” cyberattack on connected refrigerators at several major French food retailers, causing food losses and fires, and opened an investigation. Carrefour said 80 of its supermarkets were hit, and Monoprix told Reuters that 5% of its roughly 490 stores were affected. Cooperative U confirmed an attack to AFP, and E. Leclerc said a cyberattack on one of its refrigeration equipment suppliers had disrupted several stores. Intermarché’s chief executive, Thierry Cotillard, told BFM TV the losses would run to “tens of millions of euros nationwide in a single day.”
The counts don’t all agree. Les Mousquetaires gave Reuters a figure of about 150 Intermarché stores, while the retailers told AFP that at least 300 Intermarché and Netto shops were targeted, along with more than 100 Cooperative U outlets.
No one has claimed the attack, and French authorities haven’t named a suspect.
Danfoss controllers and outdated firmware
Prime Minister Sébastien Lecornu ordered ANSSI, France’s national cybersecurity agency, to investigate. A person in his office told reporters the agency had found a vulnerability in software from Danfoss, the Danish refrigeration manufacturer, had contacted the company, and was working with other European agencies in case other countries were hit. Félix Aimé, an analyst at the French security firm Sekoia, told Reuters that Spain, Portugal, Poland, Germany and Belgium were also affected. No government in those countries has confirmed that as of this writing.
Danfoss said the affected units were running outdated firmware. In a statement to AFP, it said most of them were legacy products that “no longer receive software or security updates,” and named its AK-SM800 and AK-SC355 refrigeration control systems among those affected. The company said it had long advised customers to update or replace them. It didn’t say how many systems were hit. France’s retail federation, the FCD, called on Danfoss for full transparency, Reuters reported.
A supermarket’s cold aisles are usually run from a single control panel that manages every fridge and freezer in the store. Many of those panels can be reached over the internet so that maintenance contractors can adjust them remotely.
The May 2025 advisory on Danfoss system managers
The U.S. government flagged flaws in Danfoss refrigeration controllers well before Monday. On May 20, 2025, the Cybersecurity and Infrastructure Security Agency (CISA) published advisory ICSA-25-140-03 on the Danfoss AK-SM 8xxA series, the system managers that run a store’s refrigeration. Its risk assessment was blunt: “Successful exploitation of these vulnerabilities could enable a remote attacker to bypass authentication and remotely execute arbitrary code.”
The first flaw, CVE-2025-41450, was a login bypass “caused by datetime-based password generation” in versions before R4.2. In August 2025 CISA updated the advisory with two more. One let an attacker who was already logged in run commands on the device through the alarm-to-mail settings. The other could be used to knock the web interface offline. Danfoss fixed the first in firmware R4.2 and the other two in R4.3.1. At the time, CISA said no public exploitation targeting the flaws had been reported to it and that they had “a high attack complexity.” The advisory credits Tomer Goldschmidt of Claroty Team82, a security research group, with reporting them.
Claroty published the full technical account on Aug. 9, 2026. The researchers found a hidden “code-of-the-day” login, apparently meant for vendor support, that accepts a password generated from the device’s date instead of the administrator’s. Anyone who rebuilt the algorithm could log in as an administrator on any day. Before reverse-engineering the firmware, they searched the internet-scanning services Shodan and Censys and found “thousands of publicly accessible management interfaces.”
Neither ANSSI nor Danfoss has said whether these were the flaws used in France.
Danfoss’s list of affected models names the AK-SM800 without the “A,” and the public statements don’t settle whether those units fall under the 2025 advisory. Danfoss’s account so far, unpatched or unsupported equipment left online, fits the risk the advisory described. It doesn’t confirm the same flaw.
Six commissaries, three investigations, no findings
Reuters noted that the French attack resembles outages at about a dozen U.S. military commissaries in late August. Starting Aug. 26, at least six of the military grocery stores told customers they couldn’t sell meat, dairy, produce or frozen food, Stars and Stripes reported. The list included Fort Irwin in California, F.E. Warren Air Force Base in Wyoming, Naval Station Newport in Rhode Island and Fort Huachuca in Arizona. Military Times added Holloman, Little Rock and Robins Air Force Bases. At Fort Huachuca, every freezer went into defrost mode overnight. “ALL frozen food has spoiled,” the base posted.
The Pentagon said almost nothing.
A defense official acknowledged a possible refrigeration disruption at some commissaries, said products were being moved to other refrigerated sites, and added, “Beyond this we have nothing additional to provide,” according to Military Times. The services and the commissary agency referred questions to the Pentagon, which didn’t answer whether there were concerns about unauthorized access, Stars and Stripes reported.
By Sept. 1, three military criminal investigative bodies had confirmed active cases: the Army Criminal Investigation Division’s Cyber Field Office, the Air Force Office of Special Investigations and the Defense Criminal Investigative Service, which the Air Force said is leading. Army CID’s cyber office handles computer intrusions and other malicious cyber activity. None of them described the investigation. As of Sept. 30, no findings had been announced, Stars and Stripes reported.
Stars and Stripes also reported that the commissary agency’s contract request for refrigeration required remote monitoring and control systems, run from a master control system in the United States. Neither the Pentagon nor the commissary agency has named the equipment vendor or a cause. Separate cooler outages at four commissaries in Germany and England in September were caused by worn equipment and slow parts deliveries, an agency spokesman said, and he called them unrelated to the U.S. cases.
| Date | Event | Source |
|---|---|---|
| May 20, 2025 | CISA advisory on Danfoss AK-SM 8xxA login bypass | CISA ICSA-25-140-03 |
| Aug. 26, 2025 | Advisory updated with two more flaws | CISA, Update A |
| Aug. 9, 2026 | Claroty publishes “code-of-the-day” research | Claroty Team82 |
| Aug. 26, 2026 | Commissary freezers begin failing in several states | Stars and Stripes, Military Times |
| Sept. 1, 2026 | Three military agencies confirm investigations | Stars and Stripes |
| Oct. 11–12, 2026 | Fridges heated at hundreds of French supermarkets | Paris prosecutor, retailers |
A second large grocer reported trouble the same day. Ahold Delhaize, which owns Albert Heijn in the Netherlands and Stop & Shop, Giant, Hannaford and Food Lion in the U.S., said it had taken several systems offline over a “security issue” and paused grocery deliveries. It said there was no reason to see a link to France.
This story is developing. Store counts, the countries affected and the flaw used could all change as ANSSI and the Paris prosecutor’s investigation report. The 2025 advisory is on CISA’s website, and Claroty’s research is on Team82’s site.
Sources
- CISA, ICS Advisory ICSA-25-140-03, “Danfoss AK-SM 8xxA Series (Update A)” (May 20, 2025, updated Aug. 26, 2025), via its published CSAF record. Used for: the three flaws, affected versions, fixes, risk evaluation, exploitation status and the Claroty credit.
- Claroty Team82, “Freeze the Controller, Defrost the Food: Uncovering Vulnerabilities in Danfoss Refrigeration Controllers” (Aug. 9, 2026). Used for: the code-of-the-day login, the internet exposure and the R4.3.1 fix.
- Reuters via KFGO, “Hackers heat French supermarket fridges, sparking fires and spoiling food” (Oct. 12, 2026), also via CNN. Used for: the Paris witness, Les Mousquetaires, Carrefour and Monoprix, the prosecutor, Lecornu’s office, Sekoia, Cotillard, Danfoss’s firmware statement, the FCD, the commissary comparison and Ahold Delhaize.
- CBS News, with AFP, “Hackers turn up the heat in refrigerators at hundreds of supermarkets in France” (Oct. 12, 2026). Used for: the AFP store counts, E. Leclerc and Cooperative U, Danfoss’s legacy-model statement, the prosecutor’s investigation and ANSSI’s contact with the vendor.
- Stars and Stripes, “Commissaries across the US affected by refrigeration outages” (Aug. 28, 2026). Used for: the six confirmed stores, the Fort Huachuca post, the unanswered questions and the remote-monitoring contract requirement.
- Stars and Stripes, “Army, Air Force special agents investigate refrigerator outages affecting several commissary stores” (Sept. 1, 2026). Used for: the three investigations, DCIS’s lead role and the unanswered access question.
- Stars and Stripes, “Refrigeration failures affect 4 military commissaries in Europe” (Sept. 30, 2026). Used for: the European outages, the spokesman’s explanation and the lack of findings.
- Military Times, “DOD confirms refrigeration disruption at military commissaries” (Aug. 28, 2026). Used for: the defense official’s statement and the additional bases.